
Incorporating our Privacy Policy
The Positive Aspirations Group Data Protection Officer is: Melanie Yearwood
Introduction, Aims and Objectives
The Positive Aspirations Group is made up of Greater London Fostering, Fostering Hearts, and Southcoast Fostering Agencies. The Positive Aspirations Group recruits and assesses high quality Foster Carers, ensuring that such Foster Carers receive a high level of support in carrying out their responsibilities to meet the needs of the children placed in their care.
In doing this, it is necessary for the PA Group to collect, store and maintain information about Foster Carers, potential Foster Carers, children and young people placed with the PA Group and people who work for the PA Group. Although there is a requirement for this information to be kept in accordance with the provisions of the Data Protection Act 2018 (DPA 2018), the PA Group regards those provisions as the minimum required and seeks to build upon them in order to implement best practice in relation to personal information handling.
The DPA 2018 sets out the framework for data protection law in the UK. It updates and replaces the Data Protection Act 1998 and came into effect on 25 May 2018.
It sits alongside the GDPR and tailors how the GDPR applies in the UK – for example by providing exemptions. It also sets out separate data protection rules for law enforcement authorities, extends data protection to some other areas such as national security and defence and sets out the Information Commissioner’s functions and powers.
The GDPR is the General Data Protection Regulation (EU) 2016/679. It sets out the key principles, rights and obligations for most processing of personal data.
This Policy is divided into a number of sections:
1. General statement
2. Privacy policy
3. Personal information handling rules (information management policy)
4. Company guidelines
5. DBS
6. Access to personal files
7. Reference requests and file viewing
8. Record Retention Schedule
9. Data breach
10. Data breach flowchart and template
11. Data protection agreements of third parties
Section 1
General Statement
The Directors of The Positive Aspirations Group are fully committed to continuous improvement in handling personal information and to the principle that legal requirements define only the minimum acceptable level. It is our belief that implementation of this policy will improve our service performance by ensuring that records are accurate, necessary, relevant and secure.
The Directors are committed to ensuring that personal information handling objectives are an integral part of the decision-making process when setting other service objectives.
The Directors are committed to the principle that responsibility for controlling personal information, lies with the Directors, employees and Foster Carers of the company.
The Directors are committed to maintaining effective systems of communication on personal information protection matters.
The Directors will plan, regularly review and develop the policy and ensure its implementation.
The Directors are committed to supporting the policy with adequate financial and physical resources and ensuring the competence of all employees and Foster Carers. They will support the policy with the provision of any necessary expert advice.
The Directors will recognise and encourage the involvement of employees and Foster Carers on matters of personal information handling.
All employees and Foster Carers will receive an induction. This will include an element of personal information handling training. All data sets will be inspected to identify possible risks and advice and assistance provided to enable those risks to be minimised or eliminated. This shall happen annually. The Directors shall assess the information, instruction and training requirements of all employees and Foster Carers. Employees and Foster Carers will be advised where their data sets do not meet the required standard and on ways in which the problems can be overcome.
Employees and Foster Carers are required to co-operate fully in all matters concerning personal information handling and to act at all times in accordance with legislation, instruction and training. They are to bring any concern about personal information handling to the attention of the Directors immediately.
This Policy in its entirety is to be brought to the attention of all employees and Foster Carers of the Positive Aspirations Group. Contravention of the policy by employees of the company may lead to disciplinary action in accordance with the Company’s disciplinary procedure. Foster carers who persistently refuse to cooperate with this policy may be reported to the Panel with a recommendation that they be deregistered.
An annual assessment including an audit will be made of the Company’s personal information handling. As a result of this audit there will be a review of the Personal Information Handling Policy and an Action Plan will be prepared where required. This General Statement and Policy is effective from April 2001 and will be reviewed annually and amended when identified as necessary.
Section 2
Privacy Policy
We take our legal duty for safeguarding your personal data and privacy very seriously.
This privacy policy sets out what sort of information we hold on Foster Carers, support members and people applying to become Foster Carers, why we need it, how we hold it, how we use it, who we share it with and what rights you have in relation to this information. It also covers our Children Looked After (CLA), employees and independently contracted staff.
This Data Protection Policy is also available on our agency websites:
GLF: https://www.greaterlondonfostering.org/
FH: https://fosteringhearts.co.uk/
SCF: https://southcoastfostering.co.uk/
For the purpose of data protection laws, the data controller for each agency is:
GLF: Greater London Fostering Ltd
FH: Fostering Hearts Ltd
SCF: South Coast Fostering Ltd
The PA Group is responsible for making sure that as a fostering service we comply with our legal duties about collecting, keeping and sharing your personal data. Information relating to or queries concerning data protection should be directed to:
GLF: info@greaterlondonfostering.org
FH: info@fosteringhearts.co.uk
Data Protection Principles
Under the GDPR, there are six data protection principles that we must comply with. These provide that the personal information we hold about you must be:
1. Processed lawfully, fairly and in a transparent manner;
2. Processed only for specified, explicit and legitimate purposes that have been clearly explained to you;
3. Adequate, relevant and limited to what is necessary;
4. Accurate and kept up to date;
5. Kept for no longer than is necessary;
6. Processed in a way that ensures appropriate security of the data.
‘Personal Data’ means any information relating to an identifiable person who can be identified (directly or indirectly) by reference to an identifier.
Why do we collect your personal data?
We collect and use your personal data in relation to your position as a Foster Carer, member of the fostering household, your role as a support member or a person applying to foster; we collect this data because the law requires us to do so.
Before we are allowed to approve you as a Foster Carer we must assess you to consider whether you are suitable to look after children and young people. This involves us collecting and recording a lot of personal information about you, your family and persons in your household. The law requires us to keep this information for a number of years, whether or not you end up being approved. If you are approved as a Foster Carer, we have a duty to supervise and support you to look after children, and to keep records of how we are doing that. We also have a legal responsibility to review your approval at least annually, and the information we have gathered and recorded is also used for that purpose.
What personal information do we collect?
Initial application
When processing your application to foster we collect information regarding you and your family. This includes:
• Personal details such as your full name, date of birth, ethnic origin, religion, language and your right to work in the UK and family composition;
• Your Contact Details such as your address, telephone number and email address;
• Detail about your lifestyle such as your accommodation, health, employment, current/previous relationships, previous fostering/adoption experience and financial situation;
• We also collect criminal record details.
Fostering assessment
If you continue to the assessment process, we collect information to assess your suitability to become a Foster Carer. This includes:
• Information about your identity such as your full name, title, ethnicity, sexuality, disability, marital status, date or birth, gender, languages spoken. We also verify your identity by requesting a copy of your passport, National Insurance Number, marriage/divorce certificate (if applicable), proof of address and Driving Licence.
• Data about your background such as childhood, personality family and other relationships including current and past marital status/relationships, education experience, employment/voluntary history, finances, address history and any previous fostering/adoption experiences.
• Details about your lifestyle such as your household accommodation, community, support network.
• Details about your capacity/suitability to be a Foster Carer, i.e. caring for children, providing structure, resilience, working with others, diversity and safer caring.
Your social worker will explain the assessment process to you and show you the forms we use to record these details.
We also collect ‘Criminal Records Data’ including details of any spent convictions, cautions or warnings. You will be asked to give written consent to us taking up Disclosure and Barring checks, medical and other checks and personal and other references. We are required to hold this information in your case record.
Approved Foster Carers
If you are approved as a Foster Carer, the personal information we collect and record includes:
• Financial Data such as your bank account details, Unique Tax Reference, National Insurance Number;
• ‘Criminal Records Data’ including details of any spent convictions, cautions or warnings will be updated at required intervals;
• We will continue to collect personal information including records about the children placed with you and how you care for them, training that you undertake, any changes in your health or circumstances and any complaints or allegations about you.
• Information gathered as part of the annual review process; this includes reports completed by you, your supervising social worker, your children, the children placed with you, their social workers and the reviewing officer. These documents may also be presented to the fostering panel.
• You will have regular supervision meetings and receive support from the agency Supervising Social Workers – all this information will form part of your case record.
As part of the post-approval process, we also process ‘Criminal Records Data’, Medical Checks and other checks that may be required to assess your ongoing suitability to foster; You will be asked to give written consent to these checks. We are required to hold this information in your case record.
Data kept on Family members
In assessing you to be a Foster Carer, and in working with you when you are a Foster Carer, it is necessary for us to have personal information about others in your family and/or living in your household. Most of this information will have been provided by you as part of your assessment or in supervision after you are approved, or by them directly, or very occasionally by others.
This personal information will be contained within your records, and we will not have a separate case record for your family members or household members. We ask that you inform your family and household members about this, according to their age and understanding, and tell them that they can read this privacy notice if they want to.
We collect personal data about family/household members of those wishing to become Foster Carers – this includes:
• Personal Data such as their full name, gender, date of birth;
• Information about their background and identity such as previous fostering/adoption experience, lifestyle.
We may also ask them for a reference, which will contain their personal opinion about the person applying to foster with us. Adult members of the fostering household will also be asked to give written consent to us processing Disclosure and Barring Checks and other checks that may be relevant (i.e. Local Authority Checks).
Additional Data that may be collected
We also collect the following types of data when you use our website:
• Technical Data which includes your IP address, browser type and version, time zone setting and location, browser plug-in types and any system and any other technology on the devices you use to access our website.
• We collect information on how you use our website and services.
• We collect data for marketing purposes, i.e. your preferences regarding marketing material you may receive from us and the way we communicate with you.
• We also collect, use and share statistical data. Statistical Data may be derived from your personal data but is not considered personal data in law as this data does not disclose your identity. However, if we combine or connect Statistical Data with your personal data so that it can directly or indirectly identify you, we treat the combined data as personal data which will be used in accordance with this privacy notice.
As you interact with our website or email marketing, we may automatically collect Technical Data about your equipment, browsing actions and patterns. We collect this personal data by using cookies, server logs and other similar technologies. We may also receive Technical Data about you if you visit other websites employing our cookies.
Special Category Data
Special category data relates to your racial or ethnic origin, religion; biometrics (where used for ID purposes); health and sexual orientation. We collect Special Category Data throughout various stages of the assessment and post-approval process.
We also process Criminal Offence Data including details of any spent convictions, cautions or warnings will be updated at required intervals. This information will be processed, with your consent, as part of the assessment process and post-approval process.
Failure to provide requested data
If you fail to provide certain personal information when requested or required, we may not be able to perform the contract we have entered into with you, or we may be prevented from complying with our legal obligations. This could result in you not being approved/reapproved as a Foster Carer.
How we collect your data
Much of the personal information we hold will have been provided by you, such as when you:
• Request information about becoming a Foster Carer; either directly from the agency, the agency website or via Social Media sites or third parties;
• Complete an application form to become a Foster Carer;
• Take part in the assessment process (i.e. conversations with your assessing social worker).
• Take part in supervision sessions or other meetings and training;
• Communicate with us by phone, email or letter;
• Subscribe to our services or newsletters or when you request marketing material to be sent to you.
Other information will come from third parties during the assessment such as criminal records checks, medical assessments or from personal referees, employers, local authorities – but only where you have given consent for us to approach them.
How we use your personal data
We will only use your personal data when the law allows us and in the following circumstances:
• You have given us consent;
• We need to comply with a legal requirement;
• We need to fulfil the requirements of a contract that we are about to enter into, or have entered into, with you;
• It is necessary for our lawful interest (or those of a third party) and your interests or rights do not override those interests.
We keep and use your information to enable us to run a fostering service in line with the requirements that are set out in law. This will include assessing your suitability to be a Foster Carer, presenting a report about this to our fostering panel, matching you with children who need to be fostered, supporting and supervising your activity as a foster care and formally reviewing, at least annually, your continued suitability to foster.
Use of Personal Information
We may use your personal data for different purposes; the following are a list of purposes for which we process your personal information and the lawful basis on which we rely to carry out such processing:
| Purpose | Lawful Basis |
| Direct Marketing | Consent, where we have a record that shows you have given us express consent to use your personal data |
| Process your application to foster | Necessary for the performance of the contract |
| Legal Obligation as specified in law | |
| Special Category Data that forms part of your application to foster: Processing is necessary for the purposes of Carrying out the obligations of the controller in the field of employment (i.e. legal requirements in relation to fostering) | |
| Undertaking a fostering assessment | Necessary for the performance of the contract |
| Legal Obligation as specified in law | |
| Necessary for our legitimate interest | |
| Special Category Data that forms part of your application to foster: Processing is necessary for the purpose of carrying out the obligations of the controller in the field of employment (i.e. legal requirements in relation to fostering) | |
| Criminal Offence Data that forms part of your application to foster; processing is necessary for the purpose of a contract and is also specified in law (Fostering Services Regulations) | |
| To maintain records relating to prospective Foster Carers, approved Foster Carers and children looked after | Legal Obligation as specified in law |
| Necessary for the performance of the contract | |
| Where this involves special category data, processing is necessary for the purpose of carrying out the obligations of the controller in the field of employment (i.e. legal requirements in relation to fostering) | |
| To assess your ongoing suitability as a Foster Carer and provide you with supervision and support | Legal Obligation as specified in law |
| Necessary for the performance of the contract | |
| Where this involves special category data Processing is necessary for the purpose of carrying out the obligations of the controller in the field of employment (i.e. legal requirements in relation to fostering | |
| Criminal Offence Data that forms part of your application to foster; processing is necessary for the purpose of a contract and is also specified in law (Fostering Services Regulations) | |
| Matching and placement of children/young people in your care (this involves assessing your suitability to looked after a specific child and provide details of the placement to the relevant local authority) | Necessary for the performance of the contract |
| Where this involves special category data Processing is necessary for the purpose of carrying out the obligations of the controller in the field of employment (i.e. legal requirements in relation to fostering | |
| Criminal Offence Data that forms part of your application to foster; processing is necessary for the purpose of a contract and is also specified in law (Fostering Services Regulations) |
We will only use your personal information for the purpose for which we collected it, unless we are required or permitted by law. If we need to use your personal information for any other purpose, we will contact you to explain the lawful basis required for the processing.
Your rights in relation to your personal information
Subject to certain conditions, and in certain circumstances, you have the right to:
• Request access to your personal information – this is usually known as making a data subject access request and it enables you to receive a copy of the personal information we hold about you;
• Request correction of your personal information – this enables you to have any inaccurate or incomplete personal information we hold about you corrected;
• Request erasure of your personal information – this enables you to ask us to delete or remove your personal information where there’s no compelling reason for its continued processing, e.g. it’s no longer necessary in relation to the purpose for which it was originally collected;
• Restrict the processing of your personal information – this enables you to ask us to suspend the processing of your personal information, e.g. if you contest its accuracy and so want us to verify its accuracy;
• Object to processing of your personal information – this enables you to ask us to stop processing your personal information where we are relying on the legitimate interests of the business as our legal basis for processing and there is something relating to your particular situation which makes you decide to object to processing on this ground and where we do not have compelling legitimate interests to override such objection;
• Data portability – this gives you the right to request the transfer of your personal information to another party so that you can reuse it across different services for your own purposes.
If you wish to exercise any of these rights, please email the agency in question:
GLF: info@greaterlondonfostering.org
SCF: info@scfostering.org
We may need to request specific information from you in order to verify your identity and check your right to access the personal information or to exercise any of your other rights. These rights are not absolute and there may be certain circumstances where we are unable to comply with your request; in such cases, we will explain why we cannot comply with your request.
Who has access to your data?
Employees (including independent workers) of the PA Group will have access to your information for the legitimate purposes set out above.
Additionally, we may share your information with third parties in certain situations:
• To undertake checks and references (i.e. medical assessment, DBS checks, personal/employment references) as part of the fostering assessment and ongoing suitability assessment, and only where you have explicitly consented to this;
• With members of our fostering panel at the time of your approval and at subsequent reviews – your information will also be shared with Reviewing Officers as part of the review process;
• With local authority commissioning services who are considering whether you might be suitable to foster a specific child they are seeking to place;
• With external inspectors (i.e. Ofsted or Local Authorities) when they are inspecting the fostering service as required by law or contract;
• With Ofsted when we submit notifications in accordance with Regulation 36 of the Fostering Services Regulations;
• With the Independent Review Mechanism if you ask for a review of any decision by the fostering service about your suitability or continued suitability to foster;
• Where required, we will pass information we hold about our Foster Carers to organisations such as Fostering Talk to register you with them as a member of our agency;
• Where required, i.e. in relation to a claim, we will also share the relevant information about our Foster Carers with our insurers;
• HM Revenue & Customs;
• With other fostering/adoption agencies when providing written references and only where you have provided consent to this.
We may make information available to regulatory authorities, governmental organisations, or other third parties if required to do so by any regulatory or legal authority, safeguarding enquiry or in order to comply with the law, or in some circumstances if you ask us to do so.
Keeping your personal data safe
We have a range of policies and controls in place to try to ensure that your data is not lost, accidentally destroyed, misused or disclosed. We have a system to ensure that your information is accessed only by individuals authorised by us to do so in the performance of their duties.
Where we are required to share your information with others, we will take reasonable technical and organisational precautions to prevent the loss, misuse or alteration of your personal information. All of our staff are trained in data protection duties, and are required to comply with our data protection policies.
The third party organisations with whom we may share your information are also bound to comply to the Data Protection Act 2018 and have appropriate policies in place to duly protect your information.
The PA Group outsources our IT services to a third-party specialist whose signed declaration confirms that whilst they need access to our system in order to support us, they will not access any information, unless the support they are providing is specifically to resolve an issue with a document or a data entry.
If there is a data breach, where we ‘lose’ or wrongly share any of your personal information by mistake, we will inform you of that, and tell you what action we are taking.
Data retention – how long do we keep it?
The law is very clear that personal data should not be kept longer than is necessary, but in relation to fostering we are required to hold data for a set minimum period of time.
For approved Foster Carers, the case record must be kept for a minimum of ten years from the date on which you ceased to foster. The PA Group’s policy is to retain personal information for up to twenty years.
Where a person has applied to foster, but for whatever reason has not gone on to be approved, the case record will be held for up to four years from the date when it was decided that the application would not proceed.
Where a person has enquired about fostering, but for whatever reason has not gone on to apply to be a Foster Carer the records of your enquiry will be kept for up to 24 months from the point of your last contact with the PA Group.
Accessing your information
You can ask to see what personal information we hold about you. This is sometimes called a subject access request (SAR). We will provide this information to you within 1 month, and there is no cost for this. If you want to see the information we hold about you then please contact the agency directly. You do not have to give any reasons for why you want to see this information but your request will be required in writing.
Looked After Children
The PA Group is provided with and collate information about you in order to find you a foster family and to support your wellbeing and progress whilst in our care. Once in our care the agency and your Foster Carer will hold information and records about you which will be kept safe and only shared with those appropriate and relevant to your placement.
Our Foster Carers are given training to ensure that their record keeping and retention of information is in line with our data protection principles.
You have a legal right to see the information that we hold about you but not information about other people.
However, the agency will retain details of reports and information that we have authored or produced on your file for 20 years or up until your 25th birthday whichever is sooner to allow you access to your records, where after they will be deleted.
Should you prefer these records to be deleted before this date, you may contact us at any point after your 18th birthday.
Working for the PA Group
Applications for employment
Where a person has applied (unsuccessfully) to work for the PA Group we will retain application forms for a period of up to 2 year in the event that we may contact you regarding future roles at the PA Group. After this period the application form shall be deleted.
The PA Group staff and independent workforce
The PA Group personnel files contain personal information in line with Ofsted’s Schedule 1 compliance regulations. This includes details of identification, work history, references, health, address, nationality etc. In addition, personnel files contain information in relation to your tenure at the PA Group, this would include supervisions, appraisals and performance related documentation where applicable. Furthermore, in order to allow for payment of salaries, the PA Group hold information on National Insurance Numbers, Bank Account details and pension contributions.
All personnel files are held securely with access limited to HR and Management. Employment Regulations suggest that personnel details should be retained for a minimum of 6 years. It is the PA Group’s policy to retain personnel files for up to 7 years. A full reference will only be provided to prospective employers during this period if written consent is received from the employee either generically at the point of resignation or individually for each reference request received thereafter.
Post this period we shall only retain details of your name, dates of employment and reason for leaving. All other information will be deleted. Any reference provided will be based on the limited data retained.
Use of CCTV and other Recording Devices
There is CCTV in the communal areas of our three other rented offices, managed by other companies.
We advise Foster Carers that if they use CCTV for security on the outside of the home, including video doorbells, they should ensure that everyone in the home including foster children know this. If Foster Carers want to use CCTV inside the home, including recording devices like baby monitors, it must never be covert (i.e. people don’t know about it) and the use needs to be approved by their supervising social worker and LA social workers of children that are have placed with them. If Foster Carers have CCTV inside the home, it should be restricted to hallway and/or pointing at areas of security, such as doors or windows and must never be used to supervise children or young people.
Use of cookies
Cookies are small files of letters and numbers stored on a person’s computer (or tablet/mobile phone) which allow us to recognise and track users of our website.
We don’t use any cookies to collect or monitor data about yourself for remarketing purposes.
The only cookies which are on our site are functional and can’t be deactivated. They allow us to do things like, provide a web chat. We sometimes use cookies to record your interactions with our websites. This is used to understand how people interact with the website and improve our website design. We do not allow you to opt out of these however, we do not track personally identifiable information this way. Cookies might be used by search engines like bing, google or social media platforms like facebook. If you have reached our site from one of these sites, we do not gather or use this information. These sites allow you to opt out of cookies, if you so wish.
For more information on managing Cookies, please follow this link:
https://ico.org.uk/for-the-public/online/cookies
International Transfers
The only circumstances where we may transfer data outside of the EEA (European Economic Area) is in relation to external websites (like Survey Monkey) that transfers some data to the United States. We always ensure that external websites have a Privacy Policy in place which is compliant with GDPR.
External Websites
Our website sometimes include links to other third-party websites which are not within our control. Once you have left our website, we cannot be held responsible for the content of these third-party websites or the protection and privacy of any information that you provide to those websites.
Comments and concerns
If you have any concerns or comments about how we use your information, we would like to hear from you. Please contact the Data Protection Officer whose details are provided earlier in this notice. Alternatively, you may contact the Information Commissioner’s Office helpline on 0303 123 1113 or visit their website: https://ico.org.uk/global/contact-us/ for guidance and advice, or to lodge a complaint:
ICO
Wycliffe House
Water Lane
Wilmslow
Cheshire SK9 5AF
Section 3
Personal information handling rules – Information management
The PA Group takes the management of all information seriously and has put this policy in place to ensure staff and those involved in the PA Group are fully aware of their information management responsibilities. Information and records are our organisation’s memory, providing evidence of actions and decisions and representing a vital asset to support daily functions and operations. Records support policy formation and managerial decision-making, protect the interests of the organisation and the rights of our children and young people, Foster Carers and staff. Our records support consistency, continuity, efficiency and productivity and help deliver services in consistent and equitable ways.
It is important to ensure information and records are:
• available when needed so that events or activities can be followed through and reconstructed as necessary;
• accessible, located and displayed in a way consistent with their initial use, with the original/current version being identified where multiple versions exist;
• able to be interpreted and set in context: who created or added to the record and when, during which business process, and how the record is related to other records;
• trustworthy and hold integrity, reliably recording the information that was used in, or created by, the business process;
• maintained over time, irrespective of any changes of format so that they are available, accessible, able to be interpreted and trustworthy;
• secure from unauthorised or inadvertent alteration or erasure, with access and disclosure being properly controlled and audit trails tracking use and changes;
• held in a robust format which remains readable for as long as records are required;
• Retained and disposed of appropriately using documented retention and disposal procedures, which include provision for reviewing and permanently preserving records with particular archival value.
The PA Group is committed to ensuring that information, in whatever its context, is processed as determined by prevailing law, statute and best practice.
The Information Management Policy sets out the PA Group’s obligations in relation to the handling of all information, including information considered to be confidential, sensitive or personal.
How we class information
| General non-sensitive | This is information which contains no personal nor sensitive information, and can be shared bother internally and externally with no encryption or permission needed. Examples include, Our guide to fostering |
| Sensitive Commercial | This is information which does not contain personally sensitive information, but contains commercially sensitive information which should not be shared externally without approval. Internal policies and procedures Pricing schedules Commercial agreements with contractors Communications with external parties in relation to commercial negotiations |
| Sensitive 3rd Party Personal | This is information which contains personal information about our Foster Carers, children in our care, or associated individuals. This information should not be shared externally unless permission is granted, and it is shared in a secure manner. This information can be accessed by authorised members of staff using our content management system. Examples include: Case recordings in regards to families Documents provided by our local authority partners in relation to case work |
| Sensitive Staff Personal | This is information relating to a member of staff, and should not be shared internally except with directors, line managers of an HR professional. It should never be shared externally except without consent of the staff member. Examples include References/ DBS disclosures |
All sensitive information must be handled and stored in the following spirit.
- No sensitive information must be left on desks, either paperwork is locked away or shredded
- Only share sensitive information with people who need to know it
- If staff are sharing with external people, it must be shared in a safe way. Those sharing information via ‘dropbox storage website’ have a duty to close access to data subject’s information within reasonable timescales, never leaving access open for longer than necessary. Ensure all third-party information is removed if no consent.
- Computers which are able to access sensitive information must always be locked if the user is not in front of it.
This Policy applies to all information and locations from which the PA Group’s systems are accessed (including home use).
Where there are links to enable non-agency personnel/organisations to have access to Greater London Fostering’s information, the PA Group must confirm the security policies they operate meet our security requirements.
Compliance
As a Fostering Agency, we are custodians of highly personal and sensitive information concerning our Foster Carers and the children in their care. We bear a duty and obligation to ensure this information is never accidentally shared, lost, or misused. Our primary safeguard is to require that all work conducted on our behalf, is performed exclusively on our remote server and communication of any and all sensitive information is through an official organisation email address. This policy guarantees that documents and information are never saved, edited, or viewed directly on an individual’s laptop, PC or mobile phone, or any other personal equipment. All information should only be carried out on PA Group equipment supplied to staff members when their employment starts, this ensures that all information is always contained on our network, and not on any personal devices. When staff leave the PA Group, all PA Group equipment supplied, must be returned to us.
All staff members and contractors or others, with access to the PA Group information must comply with this policy. Anyone who is found to have breached this policy could be subject to the Positive Aspirations Group’s Disciplinary and Dismissal Policy & Procedure and serious breaches of this policy could be regarded as gross misconduct. Non-compliance with these protocols may result in immediate termination of your employment or contract, and you may be held personally liable for any damages, fines, or actions taken by the Data Commissioners Office or the injured parties. It is imperative that we all adhere to these guidelines to protect the confidentiality and integrity of the data entrusted to us. If you do not understand the implications of this or how it may apply to you, seek advice from Human Resources.
All staff members and contractors or others, engaged in handling personal information shall be required to sign a declaration stating that they have read and understood this Data Protection and Information Management policy and agreeing to keep confidential any information whatsoever that has been passed to them in connection with their employment by the Positive Aspirations Group.
All Foster Carers shall have the policy of the PA Group and these rules explained to them by their supervisor.
No personal information of any kind may be passed on to any other person unless it is necessary in order to carry out the duties of the post or there is risk of substantial harm to any person or is required by law.
No member of staff shall make any statement or comment to the press or other news media without the express consent of one or more of the Directors.
All paper files containing personal data shall be kept secure and shall only be accessible to authorised persons. This will usually require storage under lock and key.
All files held electronically containing personal data shall be kept in a secure manner and shall only be accessible to authorised persons. This will usually require passwords.
All paper files containing personal data shall be reviewed regularly to ensure that the information contained is both necessary and accurate.
All files held electronically shall be reviewed regularly to ensure that the information contained is both necessary and accurate.
All photos of people or documents held on staff or Foster Carers mobile devices relating to fostering work, should be saved to appropriate files if needed for recording purposes. Staff and Foster Carers should review photos or documents on mobile devices, at least once in any three-month period, deleting them of the mobile device or a cloud folder, when no longer needed.
All persons acting on behalf of the PA Group shall satisfy themselves that any person requesting personal information is entitled to receive that information. This is particularly important when a request for information is received by telephone. In order to guard against the wrongful disclosure of confidential information, unless the caller is satisfactorily identified, the caller should be rung back and the telephone number checked before the information is disclosed.
Where a caller’s authority to be given confidential information is not established, no information should be given. The caller should be asked to write to the PA Group so that further investigations may be made.
There will be no access to references supplied to the PA Group except where such references have been supplied on the basis that such access will be granted.
Data Subjects will be informed that information is collected about them.
No personal information held by the PA Group will be passed to any other person except with the consent of the Data Subject except where such a transfer is required by law.
All personal information no longer needed will be disposed of in a proper manner.
All reports prepared for the Panel and shared via secure site dropbox for panel members, will be deleted after two weeks of that panel date.
There are occasions when a Foster Carer, or social worker, may be asked by a child or a member of their family to keep information confidential. All Carers, social workers and others, should not agree to maintain confidentiality in the following circumstances:
• If the information given indicates that the child or any other person is at risk;
• If there is any indication that there may be criminal activity either contemplated or having happened;
• If any details given suggest that an offence may have been committed against the person or child in the past.
In any of these circumstances, the child should be told that you have a responsibility to report such matters to the agency and the placing local authority. You should listen and be sympathetic but you should not ask leading questions as this could affect any future police action. Do not prompt the child or young person. Do not be judgmental. Carers should report the matter to their supervising social worker as soon as possible.
Section 4
Company Guidelines
Training
The Board of Directors shall be responsible, in consultation with employees, agents, Foster Carers and other carers, for the identification of the training needs of employees, agents, Foster Carers and other carers.
The identification of the training needs of individual Foster Carers will take place as part of the annual review. The identification of the training needs of members of staff will take place as part of their annual appraisal.
The Directors will be responsible for drawing up and implementing a training programme, which will include training in personal information handling. Training will be undertaken as a combination of on the job training and classroom teaching.
All staff shall receive GDPR and information management handling training during the course of their induction a record of which will be retained by Human Resources.
The adequacy of the training will be reviewed by the Directors at subsequent meetings following discussion with the participants and the training programme will be reviewed annually to ensure that it capable of meeting the identified needs.
Planning
The Directors will take responsibility for preparing and implementing the Policy and Rules. They will also be responsible for leading the annual review of the policy.
Monitoring
The implementation of this policy and of the action plan will be monitored by the Directors on a monthly basis as part of the agenda for the normal meetings.
Section 5
DBS
Special arrangements relating to Disclosure Barring Service
It is a requirement of the Code of Practice that all Registered Bodies must have a written policy on the correct handling and safekeeping of Disclosure information. It also obliges Registered Bodies to ensure that a body or individual, on whose behalf they are countersigning Disclosure applications, has a written policy.
General principles
As an organisation using the Disclosure Barring Service (DBS) service to help assess the suitability of applicants for positions of trust, the Positive Aspirations Group complies fully with the DBS Code of Practice regarding the correct handling, use, storage, retention and disposal of Disclosures and Disclosure information. It also complies fully with its obligations under the DPA 2018 and other relevant legislation pertaining to the safe handling, use, storage, retention and disposal of Disclosure information and has a written policy on these matters, which is available to those who wish to see it on request.
Due to the nature of the PA Group’s work the provisions of the Rehabilitation of Offenders Act 1974 do not apply to its staff, consultants, Foster Carers and the members of Foster Carers support networks. This means that all convictions, however old, must be declared and can never be considered “spent”. Applicants should therefore provide details of all criminal convictions, cautions, binding-over or pending prosecutions. The PA Group’s policy on the recruitment of ex-offenders is set out separately but the following is a summary. People with criminal records applying for a post should be treated according to their merits and to any special criteria of the post. Having a criminal record, in itself, should not necessarily prevent a person from being appointed to any post unless the offence debars the person.
The Positive Aspirations Group undertakes to treat all applicants for positions fairly. The Positive Aspirations Group undertakes not to discriminate unfairly against any subject of a disclosure on the basis of conviction or other information revealed. A copy of the DBS Code of Practice can be supplied on request or is available from the DBSs web site.
Storage and access
Until utilised, Disclosure information should be kept securely, in lockable, non-portable, storage containers with access strictly controlled and limited to those who are entitled to see it as part of their duties.
Handling
In accordance with section 124 of the Police Act 1997, Disclosure information is only passed to those who are authorised to receive it in the course of their duties. We maintain a record of all those to whom Disclosures or Disclosure information has been revealed and it is a criminal offence to pass this information to anyone who is not entitled to receive it.
Usage
Disclosure information is only used for the specific purpose for which it was requested and for which the applicant’s full consent has been given. If an applicant reveals a serious criminal record, particularly if it is recent, Senior Managers will consider whether the offence might mean that the person presents a risk to children. If possible, an applicant in those circumstances should be advised of why their application has had to be rejected.
Disclosure information can be revealed to other government departments or in the case of an employment Tribunal. In either case permission should be sought from the DBS before any information is revealed. With the consent of the person the information can be shared with other parties.
If disclosure information is lost, the registered person should inform the Data Barring Service immediately. The Bureau will consider whether to issue a replacement if this is requested.
Retention
Once a recruitment (or other relevant) decision has been made the Positive Aspirations Group do not retain original DBS certificates however, as required by Ofsted we will record your name, date of birth, disclosure number and date of certificate. We will record whether the result was a Match/No Match. If a Match, details of the Match information will also be recorded as part of a risk assessment process. This information will be retained on the subjects file.
Section 6
Access to Personal Files (Subject Access Requests) Introduction and Principles
Introduction and Principles
The Positive Aspirations Group supports a policy of open information except where such a policy conflicts with the safeguarding of the interests of the children and young people placed with the agency.
The Data Protection Act 2018 sets out a number of principles for the handling of Data. The Positive Aspirations Group will seek to build on those principles and will seek to adopt the best practice in handling personal data relating to the children and young people in its care, potential, actual and past Foster Carers and staff and other people connected with the PA Group.
Who has Access?
All data subjects will, subject to the conditions given below, have the right of access to information held by the PA Group on them. Where more than one file is maintained access shall be given to all such files, including those held electronically. Where files are not held in the same place the data subject shall be informed of their existence and asked whether access is required. If such access is required they shall be moved to a common location for inspection.
Access to a file will be limited to the individual data subject only. With the written consent of the Data Subject, this right may be extended to the Data Subject’s representative.
In cases where data subjects are incapable of understanding or exercising their rights, for example, because they are too young or suffer from a severe mental handicap, then subject access requests may be made by parents or other persons who are legally able to act on behalf of the data subject. In such a situation the PA Group reserves the right to refuse access unless it is satisfied that the request has been made by a person acting in the data subjects’ interest.
What information is access to be given to?
In accordance with DPA 2018, Data Subjects are entitled to be told if any personal data are held about them and, if it is –
- To be given a description of the data;
- To be told why the data is held;
- To be told who the data may have been given to;
- To be given a copy of the data with any technical terms explained;
- To be given any information available to the Data Controller as to the source of the data;
- To be given an explanation as to how any automated decision taken about them have been made.
The PA Group reserves the right to withhold information in the following circumstances:
- If the information on a file identifies other people, then it will often be right to remove that information unless the third parties have agreed to the disclosure;
- If the disclosure of the information would prejudice the carrying out of social work by reason of the fact that serious harm to the physical or mental health of the data subject or any other person would be likely to be caused;
- If in the case of requests made on behalf of the data subject by a person able to exercise their legal rights, the data subject has expressly asked that some or all of the information should not be disclosed or if they have provided the Social Services Department with information on the assumption that it will not be disclosed;
- If the personal information consists of information as to whether the Data Subject is or has been the subject of or may be at risk of child abuse and where access would not be in the best interests of the data subject.
- If in that particular case it would hinder the prevention and detection of crime or the prosecution or apprehension of offenders to provide it.
- There will be no access to confidential medical records, either from the agency’s Medical Advisor or from the Data Subjects own doctor except where such records have been supplied on the basis that such access will be granted.
- There will be no access to references supplied to the agency except where such references have been supplied on the basis that such access will be granted.
Implementation
Access to personal files will require the data subject to complete a Data Subject Access Request. The agency is required to provide copies of the information requested within one month. Access to files will be limited to inspection only and the data subject may not remove any document. Photocopies of documents will be made available on request and, in the case of documents stored electronically, copies may be supplied either on paper or electronically.
Data Subjects may request the agency to remove documents from their personal file, or erase or block the information. If the agency is not prepared to accede to this request, the Data Subject should be given the opportunity to record on the file his/her disagreement with any document contained on the file. Any dispute on the contents of a file may be pursued through the agency’s complaints procedure or grievance procedure as appropriate. In the event of the Data Subject not being satisfied with the agency’s response, s/he should be told of her/his legal rights.
Section 7
Reference Requests and File Viewing
The agency only responds to reference requests received for Carers, Staff (including Independents) and students.
NB: No reference will be provided without written consent from the subject having been received.
NB: Where the request is for a fostering reference on a fostering household with two Foster Carers both Foster Carers shall be required to consent to the release of any information.
Foster carers
• Only approved carers/ex carers will have formal written references.
• The PA Group staff are not permitted to provide personal references.
• Fostering references will include the date of approval, date of resignation/deregistration, terms of approval, any variation, safeguarding concerns as Y/N. Where the reference is a fostering reference from another fostering service an invite to view files will also be offered – subject to further consent being received from the Foster Carer/s.
• Non-fostering references will include date of approval and date of resignation/deregistration only unless the role applied involves working with children/YP whereby safeguarding concerns as a Y/N can be provided.
File Viewing
Where a former Foster Carer has applied to join another fostering agency there may be a request to view their agency file. All requests for file viewing must be made in writing and will not be actioned until the consent of the Foster Carer/s has been received.
Staff and Independently Contracted workers
In line with employment regulations upon leaving the PA Group personnel files will be retained for a period of up to 7 years.
A full reference will only be provided to prospective employers during this seven-year period where written consent is received either generically at the point of resignation or individually for each request received thereafter.
Post the seven-year period we shall only retain details of the staff members name, dates of employment and reason for leaving. All other information will be deleted. Any reference provided will be based on the limited data retained.
Section 8
Record Retention Schedule
- Human Resource
| DOCUMENT | RETENTION PERIOD | EXTRA INFORMATION | SOURCE |
| Sickness / Sick Pay | Although it is no longer a statutory requirement to keep SSP records (gov.uk SSP: employer guide) it is recommended that records are kept for a period of 6 years after employment ceases in case of any dispute over payment of SSP or HMRC enquiry. It is the PA Group’s policy to retain personnel files for up to 7 years | N/A | The Statutory Sick Pay (General) Regulations 1982 (SI 1982/894) as amended – section 13 https://www.legislation.gov.uk/uksi/1982/894/regulation/13 The Statutory Sick Pay (Maintenance of Records) (Revocation) Regulations 2014 (SI 2014/55) http://www.legislation.gov.uk/uksi/2014/55/made Statutory Sick Pay (SSP): employer guide – gov.uk https://www.gov.uk/employers-sick-pay |
| Maternity Leave / Pay | 7 years following the end of the company financial. | N/A | The Statutory Maternity Pay (General) Regulations 1986 (SI 1986/1960) as amended – section 26 https://www.legislation.gov.uk/uksi/1986/1960/regulation/26/made Statutory Maternity Pay and Leave: employer guide – gov.uk https://www.gov.uk/employers-maternity-pay-leave/records http://www.cipd.co.uk/ (subscription required) Retention of HR Records Factsheet Protected document |
| Paternity Leave / Pay | 7 years following the end of the company financial. | N/A | Statutory Paternity Pay and Leave: employer guide – gov.uk https://www.gov.uk/employers-paternity-pay- leave/records http://www.cipd.co.uk/ (subscription required) Retention of HR Records Factsheet Protected document |
| Shared Parental Leave / Pay | 7 years following the end of the company financial. | N/A | The Shared Parental Leave Regulations 2014 (SI 2014/3050) http://www.legislation.gov.uk/uksi/2014/3050/contents/made Shared Parental Leave and Pay: employer guide – gov.uk https://www.gov.uk/shared-parental-leave-and-pay- employer-guide/record-keeping http://www.cipd.co.uk/ (subscription required) Retention of HR Records Factsheet Protected document |
| Adoption Leave / Pay | 7 years following the end of the company financial. | N/A | Statutory Adoption Pay and Leave: employer guide – gov.uk https://www.gov.uk/employers-adoption-pay- leave/records |
| Wages / Salary / PAYE | 7 years following the end of the company financial. | Taxes Management Act 1970 (SI 1970/9) – section34 http://www.legislation.gov.uk/ukpga/1970/9/section/34/enacted PAYE and Payroll for Employers – gov.uk https://www.gov.uk/paye-for-employers/keeping- records | |
| National Minimum Wage | The statutory requirement is 3 years after the end of the pay reference period immediately following the one to which they relate – However, it is the PA Group’s policy to retain this informing for up to 7 years | Statutory National Minimum Wage Act 1998 | The National Minimum Wage Regulations 1999 (SI 1999/584) – section 38 http://www.legislation.gov.uk/uksi/1999/584/regulatio n/38/made |
| Applications Forms and Interview Notes for unsuccessful candidates | Where a person has applied (unsuccessfully) to work for the PA Group we will retain application forms for a period of up to 2 years in the event that we may contact you regarding future roles at the PA Group. After this period the application form shall be deleted. | http://www.cipd.co.uk/ (subscription required) Retention of HR Records Factsheet Protected document | |
| DBS Disclosures / DBS Certificate | Once a recruitment (or other relevant) decision has been made Positive Aspirations Group do not retain original DBS certificates however, as required by Ofsted we will record the name, date of birth, disclosure number and date of certificate for 7 years. | Revised Code of Practice for Disclosure and Barring Service Registered Persons November 2015 https://www.gov.uk/government/publications/dbs- code-of-practice Guidance on Handling of DBS certificate information https://www.gov.uk/government/publications/handling-of-dbs-certificate-information (Updated 04/07/18) |
| Personnel/Staff Files including training records, disciplinary records and redundancy | The statutory requirement is 6 years after employment ceases or 75th Birthday (whichever is soonest) if a summary has been made. However, it is the PA Group’s policy to retain this information for up to 7 years. | Information Governance Alliance (IGA) https://digital.nhs.uk/data-and-information/looking- after-information/data-security-and-information- governance/codes-of-practice-for-handling- information-in-health-and-care/records-management- code-of-practice-for-health-and-social-care-2016 Appendix 3 (not in replacement doc) | |
| Staff Salary/ Information/Files | 7 years from the close of the financial year they relate. | The above does not seem to be included in the replacement doc- this entry is the closest. | Records Management Code of Practice 2020 reviewed Oct 2020 published 14dec20 https://www.nhsx.nhs.uk/information- governance/guidance/records-management-code/ |
| General Operating Policies & Procedures | 7 years from the end of the financial year to which they relate | Review and consider transfer to a Place of Deposit | Information Governance Alliance (IGA) https://digital.nhs.uk/data-and-information/looking- after-information/data-security-and-information- governance/codes-of-practice-for-handling- information-in-health-and-care/records-management- code-of-practice-for-health-and-social-care-2016 Appendix 3 (not in replacement doc) |
| Pensions – Worker / Jobholder and Pension Scheme Records | 7 years following the end of the financial year in which the employees leave | Records that must be kept by law under the new employer duties | The Pensions Regulator – Detailed Guidance for Employers – Publication 9 Keeping Records (April 2016) https://www.thepensionsregulator.gov.uk/en/document-library/automatic-enrolment-detailed-guidance/9-keeping-records |
2. Accounting & Financial
| DOCUMENT | RETENTION PERIOD | EXTRA INFORMATION | SOURCE |
| Accounting documents for a Private Limited Company | The statutory requirement is 6 years from the end of the last company financial year. However, our policy is to retain this information for 7 years from the end of the last company financial year. | HMRC can levy a fine if accounting records are not kept To cover the time limit for bringing any civil legal action against you, including national minimum wage claims and contractual claims | https://www.gov.uk/running-a-limited-company/company-and-accounting-records |
| VAT Records | 7 years from the end of the last company financial year | HMRC can charge a penalty if VAT records are not kept in order | https://www.gov.uk/vat-record-keeping |
| Tax Records | 7 years from the end of the last company financial year | HMRC can charge a penalty if company tax records are not kept | https://www.gov.uk/keeping-your-pay-tax- records/how-long-to-keep-your-records https://www.gov.uk/government/uploads/system/uplo ads/attachment_data/file/377656/rk-bk1.pdf |
| Pensions – Worker / Jobholder and Pension Scheme Records | 7 years from the end of the last company financial year | Records that must be kept by law under the new employer duties | The Pensions Regulator – Detailed Guidance for Employers – Publication 9 Keeping Records (April 2016) https://www.thepensionsregulator.gov.uk/en/document-library/automatic-enrolment-detailed-guidance/9-keeping-records |
3. Fostering
| Case Records – Prospective Foster Carer who enquired but do not apply | Where a person has enquired about fostering, but for whatever reason has not gone on to apply to be a Foster Carer the records of your enquiry will be kept for up to 24 months from the point of your last contact with the PA Group | Records must be kept securely | https://www.gov.uk/government/uploads/system/uploads/attachment_data/file/192705/NMS_Fostering_Ser vices.pdf Standards 26, 27 Underpinning Legislation.32 Retention and confidentiality of records. |
| Records – Children and Young People | The PA Group will retain details of reports and information that we have authored or produced on children file for 20 years or up until the child’s 25th birthday whichever come first | Records must be kept securely | The Fostering Services (England) Regulations 2011 – section 22, Schedule 2 http://www.legislation.gov.uk/uksi/2011/581/regulatio n/22/made http://www.legislation.gov.uk/uksi/2011/581/schedule/2/made Fostering Services: National Minimum Standards https://www.gov.uk/government/uploads/system/uploads/attachment_data/file/192705/NMS_Fostering_Ser vices.pdf Standards 26, 27 Underpinning Legislation.32 Retention and confidentiality of records. |
| DOCUMENT | RETENTION PERIOD | EXTRA INFORMATION | SOURCE |
| Case Records – Foster Carer – Approved | For approved Foster Carers, the case record must be kept for a minimum of 10 years from the date on which you ceased to foster. The PA Group’s policy is to retain personal information for up to 20 years. | Records must be kept securely and not disclosed to any person unless required by law or court order EXCEPT in the case of sharing information with another fostering service to support the assessment of a person’s suitability to foster (Reg 32(6)) as specified in the Statutory Guidance. All parties must give prior consent. | The Fostering Services (England) Regulations 2011 – section 32 http://www.legislation.gov.uk/uksi/2011/581/regulatio n/32/made Fostering Services: National Minimum Standards https://www.gov.uk/government/uploads/system/uploads/attachment_data/file/192705/NMS_FosteringServices.pdf Standards 26, 27 Underpinning Legislation.32 Retention and confidentiality of records. Statutory Guidance on Assessment and Approval of Foster Carers https://www.gov.uk/government/uploads/system/uploads/attachment_data/file/275764/20130522statutory_guidanceassessment_and_approval_of_foster_carers_final.pdf |
| Case Records – Prospective Foster Carer – Not Approved or Withdrawn prior to Approval | Where a person has applied to foster, but for whatever reason has not gone on to be approved, the case record will be held for up to 4 years from the date when it was decided that the application would not proceed. | Records must be kept securely and not disclosed to any person unless required by law or court order EXCEPT in the case of sharing information with another fostering service to support the assessment of a person’s suitability to foster (Reg 32(6)) as specified in the Statutory Guidance All parties must give prior consent. | The Fostering Services (England) Regulations 2011 – section 32 http://www.legislation.gov.uk/uksi/2011/581/regulatio n/32/made Fostering Services: National Minimum Standards https://www.gov.uk/government/uploads/system/uploads/attachment_data/file/192705/NMS_Fostering_Ser vices.pdf Standards 26, 27 Underpinning Legislation.32 Retention and confidentiality of records. Statutory Guidance on Assessment and Approval of Foster Carers https://assets.publishing.service.gov.uk/government/uploads/system/uploads/attachment_data/file/275764/20130522statutory_guidanceassessment_and_approval_of_foster_carers_final.pdf |
4. Insurance
| DOCUMENT | RETENTION PERIOD | EXTRA INFORMATION | SOURCE |
| Employers’ Liability | The requirements to retain compulsory employers’ liability certificates for 40 years ceased on 1 October 2008. However, we will continue to saving them for 40 years. | ELTO Employers Liability Tracing Office now hold consolidated database. | https://www.gov.uk/employers-liability-insurance Employers’ Liability (Compulsory Insurance) Act 1969 – A brief guide for employers http://www.hse.gov.uk/Pubns/hse40.pdf Code of Practice for Tracing Employers’ Liability Insurance Policies https://www.gov.uk/government/publications/code-of-practice-for-tracing-employers-liability-compulsory-insurance-policies Now superseded by ELTO Employers Liability tracing Office. https://www.elto.org.uk/home/ |
5. Health & Safety
| DOCUMENT | RETENTION PERIOD | EXTRA INFORMATION | SOURCE |
| Accident Books Accident Records / Reports Record of any reportable injury, disease or dangerous occurrence (RIDDOR) | The PA Group will retain this information for at least 3 years. It will be deleted in the December following the 3rd year anniversary of the event having been recorded | Brief guide to RIDDOR https://www.hse.gov.uk/pubns/indg453.pdf HSE Information Sheet Reporting injuries, diseases and dangerous occurrences in health and social care http://www.hse.gov.uk/pub ns/indg453.htm | The Reporting of Injuries, Diseases and Dangerous Occurrences (RIDDOR) Regulations 2013 (SI 2013/1471) http://www.legislation.gov.uk/uksi/2013/1471/content s/made Provision 12: Recording and record-keeping. http://www.cipd.co.uk/ subscription needed Retention of HR Records Factsheet Protected document. |
6. General
| DOCUMENT | RETENTION PERIOD | EXTRA INFORMATION | SOURCE |
| Outlook – Emails across PA Group | The PA Group will retain this information within staff emails for at least 7 years. | Some emails will be saved to other folders/systems, for future reference or for regulatory purpose. | Fostering Services: National Minimum Standards https://www.gov.uk/government/uploads/system/uploads/attachment_data/file/192705/NMS_Fostering_Ser vices.pdf Standards 26, 27 Underpinning Legislation.32 Retention and confidentiality of records. Information Governance Alliance (IGA) https://digital.nhs.uk/data-and-information/looking- after-information/data-security-and-information- governance/codes-of-practice-for-handling- information-in-health-and-care/records-management- code-of-practice-for-health-and-social-care-2016 Appendix 3 (not in replacement doc) |
| CareCheck – DBS information | DBS results are purged after 180 days (90 days for Disclosure Scotland results) • After 3 years of the completion date all of the data such as the candidate’s title, name, date of birth, gender, address history, place of birth, nationality, job title, level of criminality check carried out, certificate number and issue date are removed. | https://www.carecheck.co.uk/about/policies/ |
Section 9
Data Breach
Data security breaches are increasingly common occurrences whether caused through human error or via malicious intent. As the amount of data and information grows and technology develops, there are new ways by which data can be breached. The PA Group needs to have in place a robust and systematic process for responding to any reported data security breach, to ensure it can act responsibly and protect personal data which it holds.
Aim
The aim of this policy is to set out our response to any data breach and ensure that
they are appropriately logged and managed in accordance with the law and best practice, so that:
• incidents are reported swiftly and can be properly investigated
• incidents are dealt with in a timely manner and normal operations restored
• incidents are recorded and documented
• the impact of the incident is understood, and action is taken to prevent further damage
• the ICO and data subjects are informed as required in more serious cases
• incidents are reviewed, and lessons learned
Definition
Article 4 (12) of the General data protection Regulation (“GDPR”) defines a data breach as:
“a breach of security leading to the unlawful destruction, loss, alteration, unauthorised disclosure
of, or access to personal data transmitted, stored or otherwise processed.”
The PA Group is obliged under the GDPR to act in respect of such data breaches. This procedure sets out how the PA Group will manage a report of a suspected data security breach.
The aim is to ensure that where data is misdirected, lost, hacked or stolen, inappropriately accessed or damaged, the incident is properly investigated and reported, and any
necessary action is taken to rectify the situation.
A data security breach can come in many forms, but the most common are as follows:
• Loss or theft of paper or other hard copy
• Data posted, e mailed or faxed to the incorrect recipient
• Loss or theft of equipment on which data is stored
• Inappropriate sharing or dissemination – Staff accessing information to which they are not entitled
• Hacking, malware, data corruption
• Information is obtained by deception or “blagging”
• Equipment failure, fire or flood
• Unescorted visitors accessing data
• Non-secure disposal of data
In any situation where staff are uncertain whether an incident constitutes a breach of security they must report it immediately to a member of the senior management group, who will decide.
Scope
This policy applies to all the PA Group’s information, regardless of format, and is applicable to all employees, foster carers and authorised third parties acting on behalf of the PA Group. It is to be read in conjunction with our Data Protection Policy (Incorporating the PA Group’s Privacy Policy).
Responsibilities Information users
The GDPR applies to both Data Controllers (the PA Group) and to anyone who works on our behalf. Therefore, all information users are responsible for reporting actual, suspected, threatened or potential information security incidents and for assisting with investigations as required, particularly if urgent action must be taken to prevent further damage.
Reporting a Breach – Internal
Suspected data security breaches must be reported promptly to the PA Group’s Data Protection Officer : Melanie Yearwood on 020 8347 8741 or email: Melanie@positiveaspirations.co.uk
The report must contain full and accurate details of the incident including who is reporting the incident [and what classification of data is involved]. The data breach report form should be completed as part of the reporting process.
Data breach procedure in the event of loss:
• Whoever discovers the breach inform Data Protection Officers and Senior Managers
• DPO will scope the extent of the breach, and ensure no further loss
• DPO will then identify all the people whose information is involved
• DPO will attempt to recover/ensure data is deleted
• Data subjects will be informed of the loss, as well as involved parties for instance local authorities within 24 hours of the breach discovery/
• Self-reporting to ICO will happen if “is likely to result in a risk to the freedoms and rights of natural persons” within 72 hours.
• Investigation of incident involving review of internal policies and procedures to make sure the same thing can’t happen again.
A report to the ICO must contain information as to the nature of the breach, categories of data, number of data records, number of people affected, name and contact details of our data lead, likely consequences of the breach and action taken.
We will keep a log of any data breaches, including what remedial action taken as a result of the breach.
Disciplinary
Staff, carers, or associated 3rd parties who act in breach of this policy may be subject to disciplinary procedures or other appropriate sanctions.
Section 10
Data breach procedure flowchart:
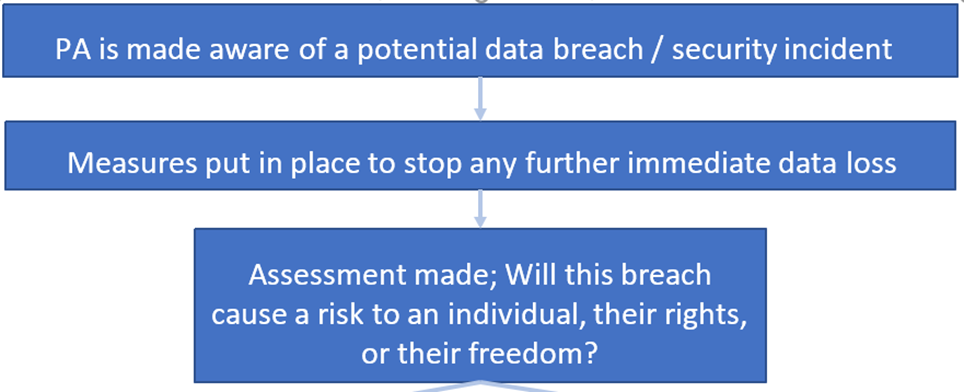
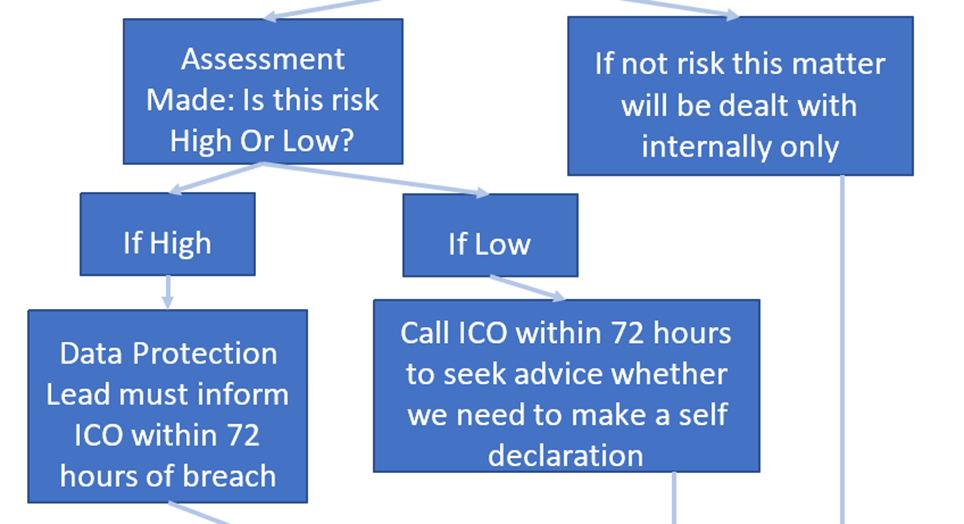
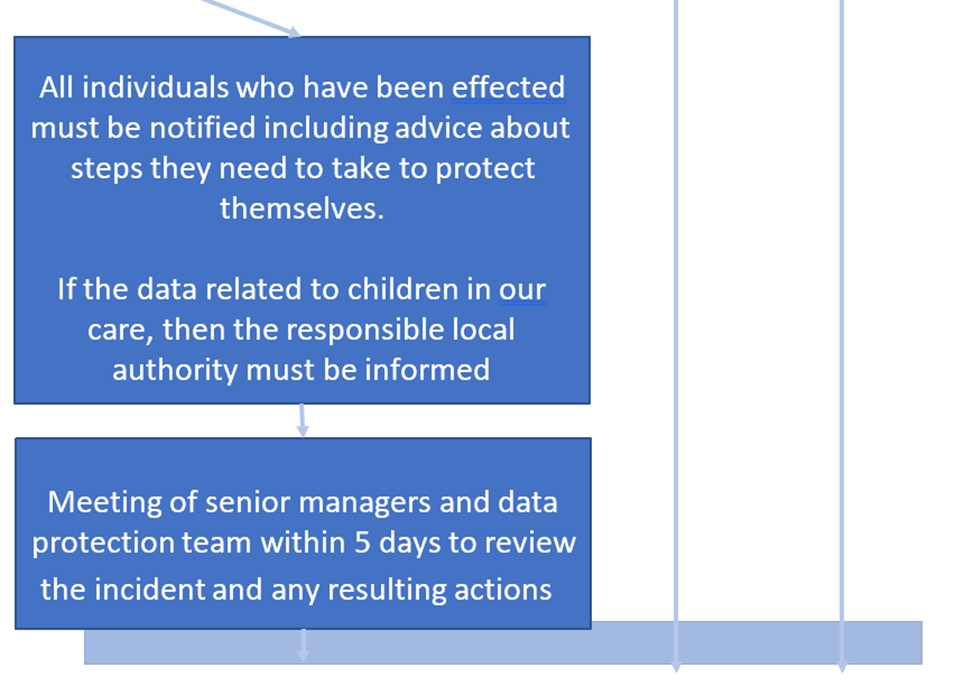
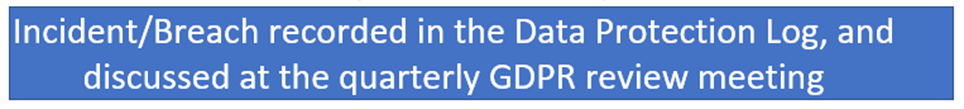
Data Breach Reporting Template:
| To be completed by the person who data breached: | |
| Today’s date? | |
| Agency? | |
| Your name? | |
| Your job title? | |
| Your line manager (if applicable)? | |
| Dates of data breach? | |
| Summary of events and circumstances, what, when, who etc? | |
| List all those involved? | |
| Type and amount of personal data shared? | |
| Type and title of document(s) shared? | |
| What information was shared? Example; name, contact details, financial, sensitive or special category data. | |
| What action did you take to rectify data breach? | |
| What action did you take to retrieve data, and respond to breach? | |
| What would have helped you, not to have data breached? | |
| Please send report, to your manager to complete the rest. If not applicable, email back to Data Protection Officer: Melanie Yearwood Melanie@positiveaspirations.co.uk and cc Tammy DeSouza Tammy@positiveaspirations.co.uk | |
| To be completed by Manager: | |
| What action was taken by Manager? | |
| Was a complaint received? Have data subjects been notified? If not, explain why not? | |
| Has there been a breach of the PA Group Data Protection and Information Management Policy and has appropriate management action been taken? | |
| Confirm date of Data Protection training by staff member? | |
| Has your team got alternative procedure/policy in place to minimise any future risk? Example: More communication, secure storage, sharing, exchange. | |
| Any further risk assessing to prevent further data loss, learning, training or system review required? | |
| Please email back to Data Protection Officer: Melanie Yearwood Melanie@positiveaspirations.co.uk and cc Tammy DeSouza Tammy@positiveaspirations.co.uk | |
| What action was taken by Data Protection Officer | |
Data protection agreements of third parties
The PA Group acts both as a Data Controller and as a Data Processor in regards to confidential and personally identifiable information dependent on whether we are producing or receiving the data. We take these roles and responsibilities seriously and at all levels are aware of our duty to protect and safeguard any and all information we hold on individuals. Data protection is more than a tick box exercise, it is a way of working, and a principle we live by. Trust is key to operating as a fostering agency, and we work every day to uphold our reputation.
We minimise the number of third parties who have access to our data, and ensure it is only shared when necessary to perform our core duties, which are to recruit, train, and support foster carers in looking after children. We do not sell, lend, or otherwise monetise data we hold.
If data is ever shared with or accessible to third parties, it is always done in line with our policies and procedures and will always follow the key principles of data protection legislation.
This policy covers when data is shared routinely, in a scheduled way, or as a one off.
- Data is only ever shared in line with at least one lawful basis.
- Data is only ever shared where is absolutely necessary, and is always done transparently, and with the understanding of the person the data is concerning.
For the purposes of this policy, we use the ICO’s (Information Commissioners Office) definition of data sharing with third parties – “The disclosure of personal data by transmission, dissemination or otherwise making it available”. This means giving personal data to a third party, by whatever means; and includes when you give a third-party access to personal data on or via your IT systems.
Ways in which the PA Group share data with third parties:
Local Authorities: As part of the process of matching a child with potential local authorities, we share information about existing foster carers, including their fostering assessment, background checks, and additional information. These documents contain personally identifiable information including sensitive personal data.
Independent Social Workers (ISWs): We use independent social workers (ISWs) for the following pieces of work:
- Fostering assessments
- Independent support for foster carers
- Annual reviews
- Ad Hoc pieces of work
All Independent Social Workers must exclusively use our system via a remote desktop environment, when accessing and completing work. This ensures that all information is always contained on our network, and not on their personal devices. ISWs are only given access to information in relation to cases they are directly working on. They do not have access to information about other people. Background checks are completed on all ISWs before they are contracted, these checks are in line with the Fostering Services (England) Regulations 2011, Schedule 1. ISWs are aware of their duties in regards to data protection and are required to sign to confirm they have read this Data Protection and Information Management Policy.
Panel Members: By law we are required to have a panel consisting of independent members. All panel members have access to specific documents regarding foster carers, such as annual reviews. The document will also reference children in a limited way. These documents are only shared via a secure platform, which prevents downloading. This ensures no documentation is ever held by the panel member for longer than is needed. Background checks are completed on all panel members before they are contracted, these checks are in line with the Fostering Services (England) Regulations 2011, Schedule 1. Panel members are aware of their duties in regards to data protection and are required to sign to confirm they have read this Data Protection and Information Management Policy.
Ofsted: We are required by law to provide Office for Standards in Education, Children’s Services and Skills (Ofsted), with both scheduled and ad hoc information. This information is in regards to staff, foster carer and the children we care for. This information is provided as part of our annual data submission, as well as on an ad hoc basis in regards to significant incidences as set out in Schedule 7 of the fostering regulations 2011. This is a legal requirement, and Ofsted’s full Data Protection Guidelines can be found at: https://www.gov.uk/government/publications/ofsted-privacy-notices/social-care-ofsted-privacy-notice
IT Support: Netflo, are an external company utilised to support our IT infrastructure. Whilst it is necessary for them to have full access to our systems and information, they are aware they should never access it, unless expressly asked to do so by ourselves in line with their support services. Their access to our system is fully auditable. Netflo does not transfer nor does it store any personal information on its systems or servers. We have a Data Protection Agreement in place with Netflo.
Microsoft: The majority of our system run off Microsoft office 365/azure networks. This includes out internally built content management system/case database. This mean there is confidential information stored by and accessible to Microsoft. Our online tools are restricted to certain IP address’, which means they are only accessible by an internal computer. As a world leader in this provision, Microsoft is fully compliant with GDPR and provides us with an extensive data protection agreement here: https://www.microsoftvolumelicensing.com/Downloader.aspx?DocumentId=16194
Pipedrive: We use Pipedrive, which is a cloud-based client relationship management software, to help us manage enquires from people wanting to foster. Data is held on this system until they either become approved foster carers, or decide they don’t want to continue with their application. As a leading CRM system, Pipedrive has a full data processing contract, which can be found at: https://support.pipedrive.com/hc/en-us/articles/360000335129-Pipedrive-and-GDPR. Data held on this system is held on Rackspace servers in Germany. No details or data on any children is held on this system.
Typeform: Typeform is a cloud-based forms system. We use this to gather feedback about placements, including processing our foster carers weekly recordings. A full data protection agreement is accessible here: https://admin.typeform.com/to/dwk6gt/. As we gather and process information about children using this tool, we minimise the amount of information in the following ways:
- As far as possible anonymising the children’s names on any information we gather
- Keeping the information in this tool for a short a period as possible, we normally delete data on a weekly basis.
- Restrict access to this platform by approved users.
Typeform hosts all its data in an encrypted form, on Amazon’s AWS servers within the EU.
Mimecast: Mimecast is an international software company that helps us secure our emails, by scanning for threats or malware. This means it has access to the content of every email we send and receive. These emails may contain sensitive information. As a large international provider of these kinds of services, Mimecast have an extensive data processing agreement, this can be downloaded at: https://www.mimecast.com/contracts/


